Homelab · Case study
3-Node Proxmox Cluster
The foundation of my lab: a three-node Proxmox VE cluster running my SIEM, automation, web and home services as VMs and containers, with approval-gated patching, a self-healing watchdog and key-only SSH.
- 3Nodes in one Proxmox VE cluster
- 28CPU threads on the largest node (i7-14700K)
- 5 minWatchdog cycle for failed guests
- 0Updates applied without my approval
Why I built it
Everything in my lab runs on this cluster: the SIEM, the automation stack, my web services and home services. I wanted it to behave like production infrastructure: segmented, monitored, patched on a schedule and able to recover on its own, without me babysitting it.
What's running
| Workload | Type | Purpose |
|---|---|---|
| Elastic SIEM | VM | Elasticsearch + Kibana for log search and investigation |
| n8n + local LLM | LXC (Docker) | Automation backend and AI-assisted troubleshooting |
| Docker host | VM | Containerized services |
| Portfolio site | LXC (Docker) | This website, in a locked-down container |
| Home Assistant | Container | Smart-home integration for the dashboard |
| Notes and web panel | VMs | Documentation and web hosting tools |
The largest node runs an Intel i7-14700K (28 threads, about 64 GB RAM), which leaves headroom for the SIEM and for running a language model locally.
How it's secured
- Nothing is exposed directly. Services are published through Nginx Proxy Manager with TLS, and the admin dashboard sits behind Cloudflare Access (zero-trust SSO).
- Segmented network. A UniFi gateway (UDM Pro Max) with VLANs and firewall rules, across 4 switches and 2 access points.
- Key-only SSH. I'm moving every node to SSH keys with password login disabled, using a separate key per workstation so one lost laptop can be revoked on its own. I'm rolling it out one node at a time, so a mistake can never lock me out of the whole cluster.
- Secrets kept out of workflows. The automation reaches Proxmox with credentials kept in n8n's encrypted store, never in workflow files or chat.
- Logging. Filebeat on each node ships logs to the SIEM over HTTPS.
How it runs itself
- Self-healing watchdog (every 5 minutes): finds guests that are set to start at boot but are down, and restarts them. Machines I shut down on purpose are left alone.
- Approval-gated patching: a nightly job checks every node, VM and container for updates, snapshots guests first, and patches nothing until I approve it. No approval means the run is skipped and logged.
- Maintenance without outages: VMs and containers reboot weekly and nodes monthly, staggered so two nodes are never down at the same time.
- Health reports: node, guest and storage health go to my dashboard, with Discord as a fallback channel.
Problems I worked through
- Right-sizing a container for a local LLM. The container running the model was starved for memory, so requests timed out. I profiled it, raised its RAM, measured token throughput and used the numbers to decide what should run locally and what should go to a hosted model.
- Keeping the SIEM stable on shared hardware. Elasticsearch takes a big share of RAM by default, so I capped its heap to keep the VM and its neighbors healthy.
- Safe change control. Snapshots before patching, human approval and staggered reboots are the same discipline as ITIL change management, applied at home.
Skills demonstrated
Virtualization (KVM/LXC) · clustering · network segmentation · hardening (SSH, least privilege) · patch and change management · monitoring and log shipping · automation · capacity planning and troubleshooting
What's next
- Finish the SSH key-only rollout on the remaining nodes.
- Add backup-restore drills to prove snapshots actually restore.
- Ship more guest logs (not just node logs) into the SIEM.
More projects
All projects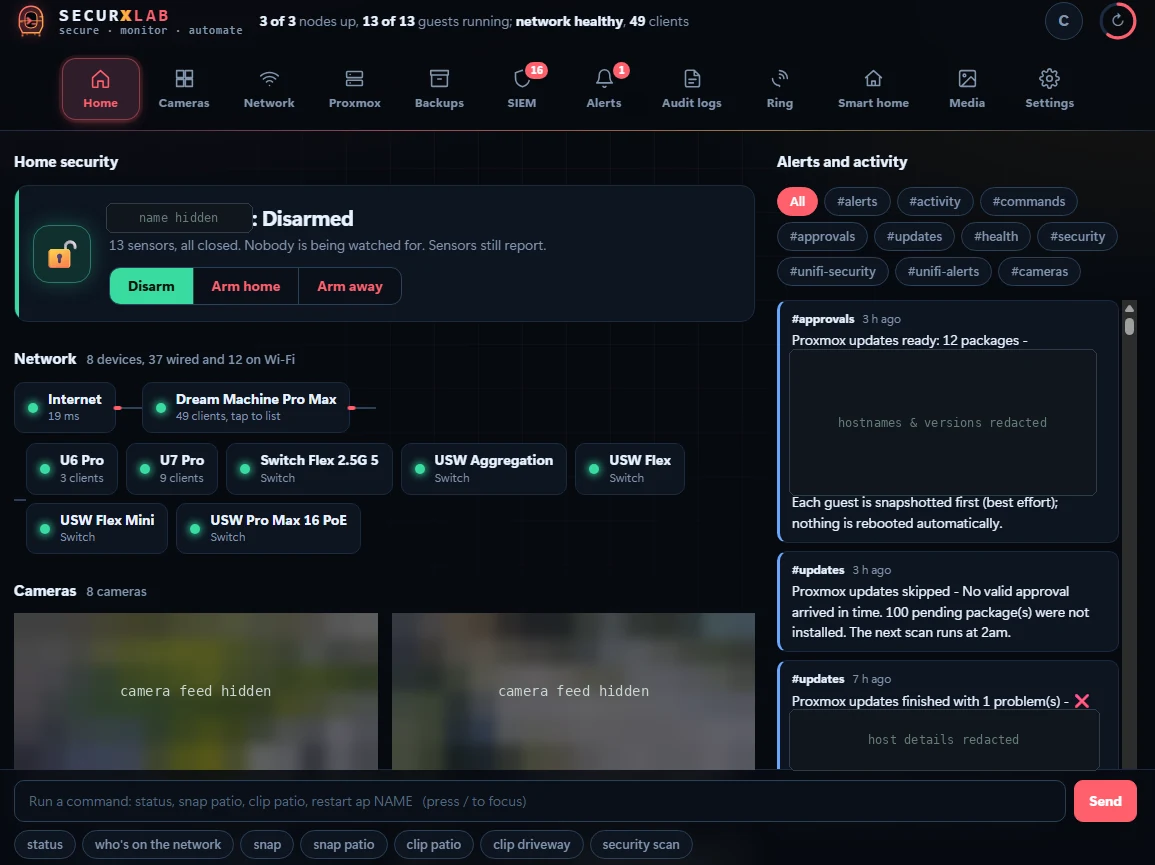 Homelab
Securxlab — Homelab SOC & Self-Healing Command Center
A self-built security operations dashboard for my homelab: SIEM with MITRE ATT&CK-mapped detections, alert triage and threat intel, plus Proxmox, UniFi and camera control, all driven by n8n automation with human-in-the-loop approvals.
Proxmox VEn8nElastic SIEMUniFi+5
Elastic SIEM + MISP
A dedicated Elastic SIEM for my lab: Filebeat ships host logs from every Proxmox node over TLS, automation events land in their own index, and MISP adds threat intelligence, all so I can investigate the way a SOC analyst does.
Elasticsearch 8KibanaFilebeatMISP+3
n8n + Discord Ops Bot
AI-assisted n8n workflows that watch my Proxmox cluster around the clock: they restart failed guests, scan for updates and wait for my approval, diagnose errors with an LLM, and report through the dashboard, with Discord as the fallback.
n8nProxmox APIOllama (llama3)Claude API+5