Cyber Lab · Case study
n8n + Discord Ops Bot
AI-assisted n8n workflows that watch my Proxmox cluster around the clock: they restart failed guests, scan for updates and wait for my approval, diagnose errors with an LLM, and report through the dashboard, with Discord as the fallback.
- 5 minWatchdog cycle
- 2:00 AMNightly update scan, patched only after approval
- 5Dedicated alert channels
- 1Real failure diagnosed and fixed by AI in testing
Why I built it
Running a cluster means a steady stream of small chores: something didn't come back after a reboot, updates are waiting, a disk is filling up. I built an operations bot that handles the routine and asks me before doing anything risky. It's the same detect → diagnose → remediate → report loop a SOC automates with SOAR.
What it does
| Workflow | Trigger | What happens |
|---|---|---|
| Updates + approval | Daily 2:00 AM | Finds updates on every node, VM and container, snapshots guests, asks for approval, patches, reports. No approval = skipped and logged. |
| Watchdog | Every 5 minutes | Restarts guests that should be running (start-at-boot) but aren't, and leaves ones I stopped on purpose alone. |
| Health report | Scheduled | Node, guest and storage health with potential problems flagged. |
| AI repair | On failure | Sends the error to an LLM, applies the suggested fix and reports the result. |
| Chat-ops | Discord command or dashboard | status, reboot, run updates and questions, answered in place. |
AI-assisted repair, proven
In a test, a VM refused to start. The workflow sent the error to the language model, which identified a stale backup lock. The workflow cleared the lock, started the VM and posted a "recovered" message, with no human involved. Anything riskier than that still waits for my approval.
Engineering decisions
- Human-in-the-loop by default. Patching and reboots need approval; only safe, reversible fixes run on their own.
- Alerts go to the dashboard first. Discord (with separate channels for alerts, approvals, updates, health and activity), ntfy and Uptime Kuma are fallbacks if the dashboard can't be reached.
- Everything is logged. Every workflow action is written to an
n8n-eventsindex in my Elastic SIEM, so automation never looks like an unexplained change. - Secrets hygiene. API keys and bot tokens live only in n8n's encrypted credential store, never in workflow JSON or chat.
Problems I solved
- Discord 403 "Missing Access." The workflow was fine; the bot lacked channel permissions. I fixed the permissions and split notifications into dedicated channels.
- LLM timeouts. The local model (llama3 8B) ran in a container with too little memory. I raised the RAM, measured throughput (about 7 seconds per token on CPU) and decided to move diagnosis to a hosted model (Claude API) for speed, keeping local inference for experiments.
Skills demonstrated
Security automation and orchestration (SOAR concepts) · REST APIs and webhooks · Proxmox administration · LLM integration · alert routing and fallback design · change control · secrets management
What's next
- Move AI steps to the Claude API for faster diagnoses.
- Add a
security scancommand: CVE and configuration checks across every node, VM and disk. - Run every command from the Securxlab dashboard's command bar, with answers shown there.
More projects
All projects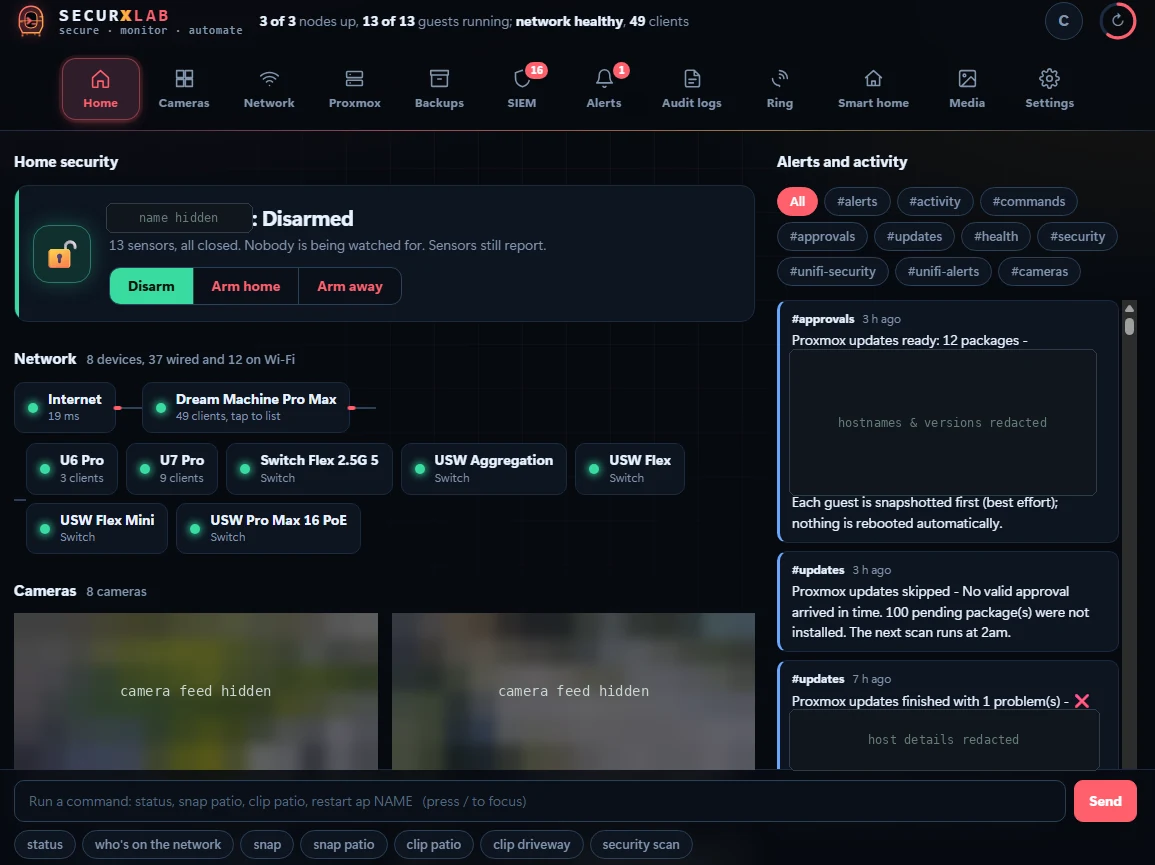 Homelab
Securxlab — Homelab SOC & Self-Healing Command Center
A self-built security operations dashboard for my homelab: SIEM with MITRE ATT&CK-mapped detections, alert triage and threat intel, plus Proxmox, UniFi and camera control, all driven by n8n automation with human-in-the-loop approvals.
Proxmox VEn8nElastic SIEMUniFi+5
3-Node Proxmox Cluster
The foundation of my lab: a three-node Proxmox VE cluster running my SIEM, automation, web and home services as VMs and containers, with approval-gated patching, a self-healing watchdog and key-only SSH.
Proxmox VEKVMLXCDocker+5
Elastic SIEM + MISP
A dedicated Elastic SIEM for my lab: Filebeat ships host logs from every Proxmox node over TLS, automation events land in their own index, and MISP adds threat intelligence, all so I can investigate the way a SOC analyst does.
Elasticsearch 8KibanaFilebeatMISP+3